
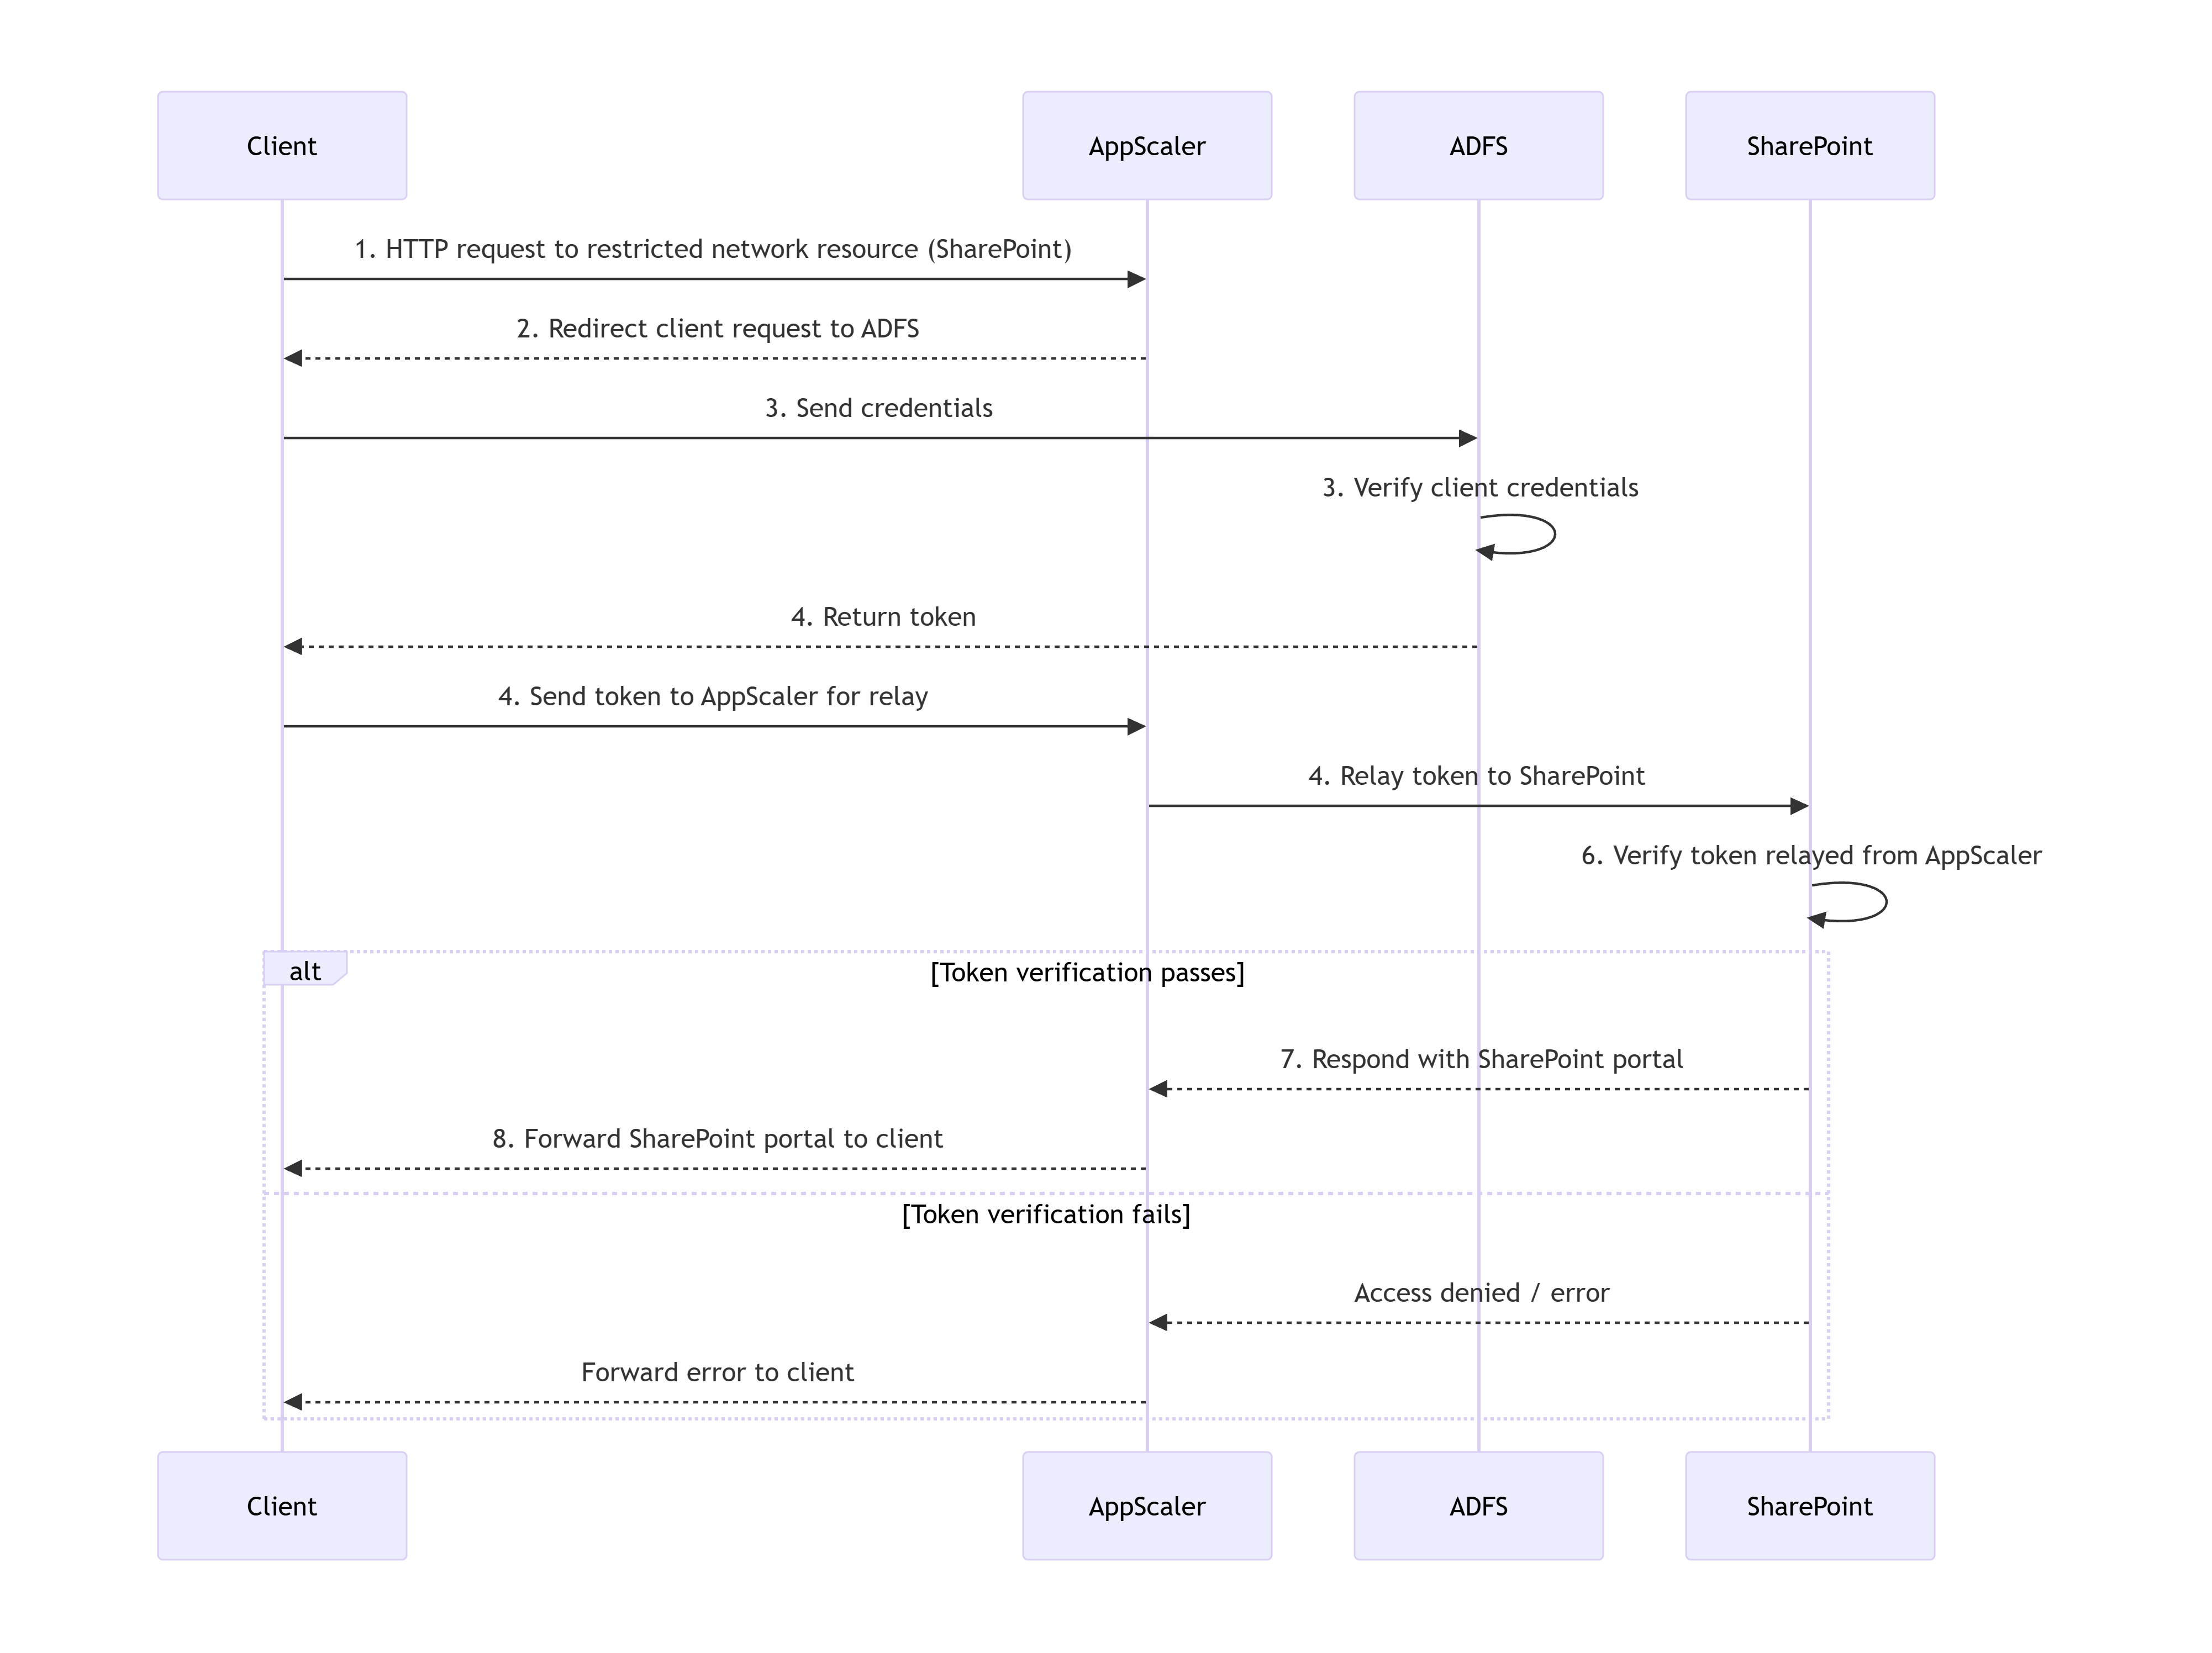
Microsoft SharePoint WS-Federation SSO
AppScaler provides the unique fit for browser-based, token-relayed access to SharePoint:
- Native Fit for SharePoint's Claims Model based on WS-Federation Passive Requestor Profile (WS-F PRP)
- Claims-Based Authorization at SharePoint
- Stateless Token Relay Through AppScaler
- Both authentication and authorization are performed using SAML
- Cross-Organization & Multi-Vendor Interoperability
- Browser-Only, No Smart Client Required
- Eliminates Complex Desktop SSO Setups
- Hybrid Identity Bridge
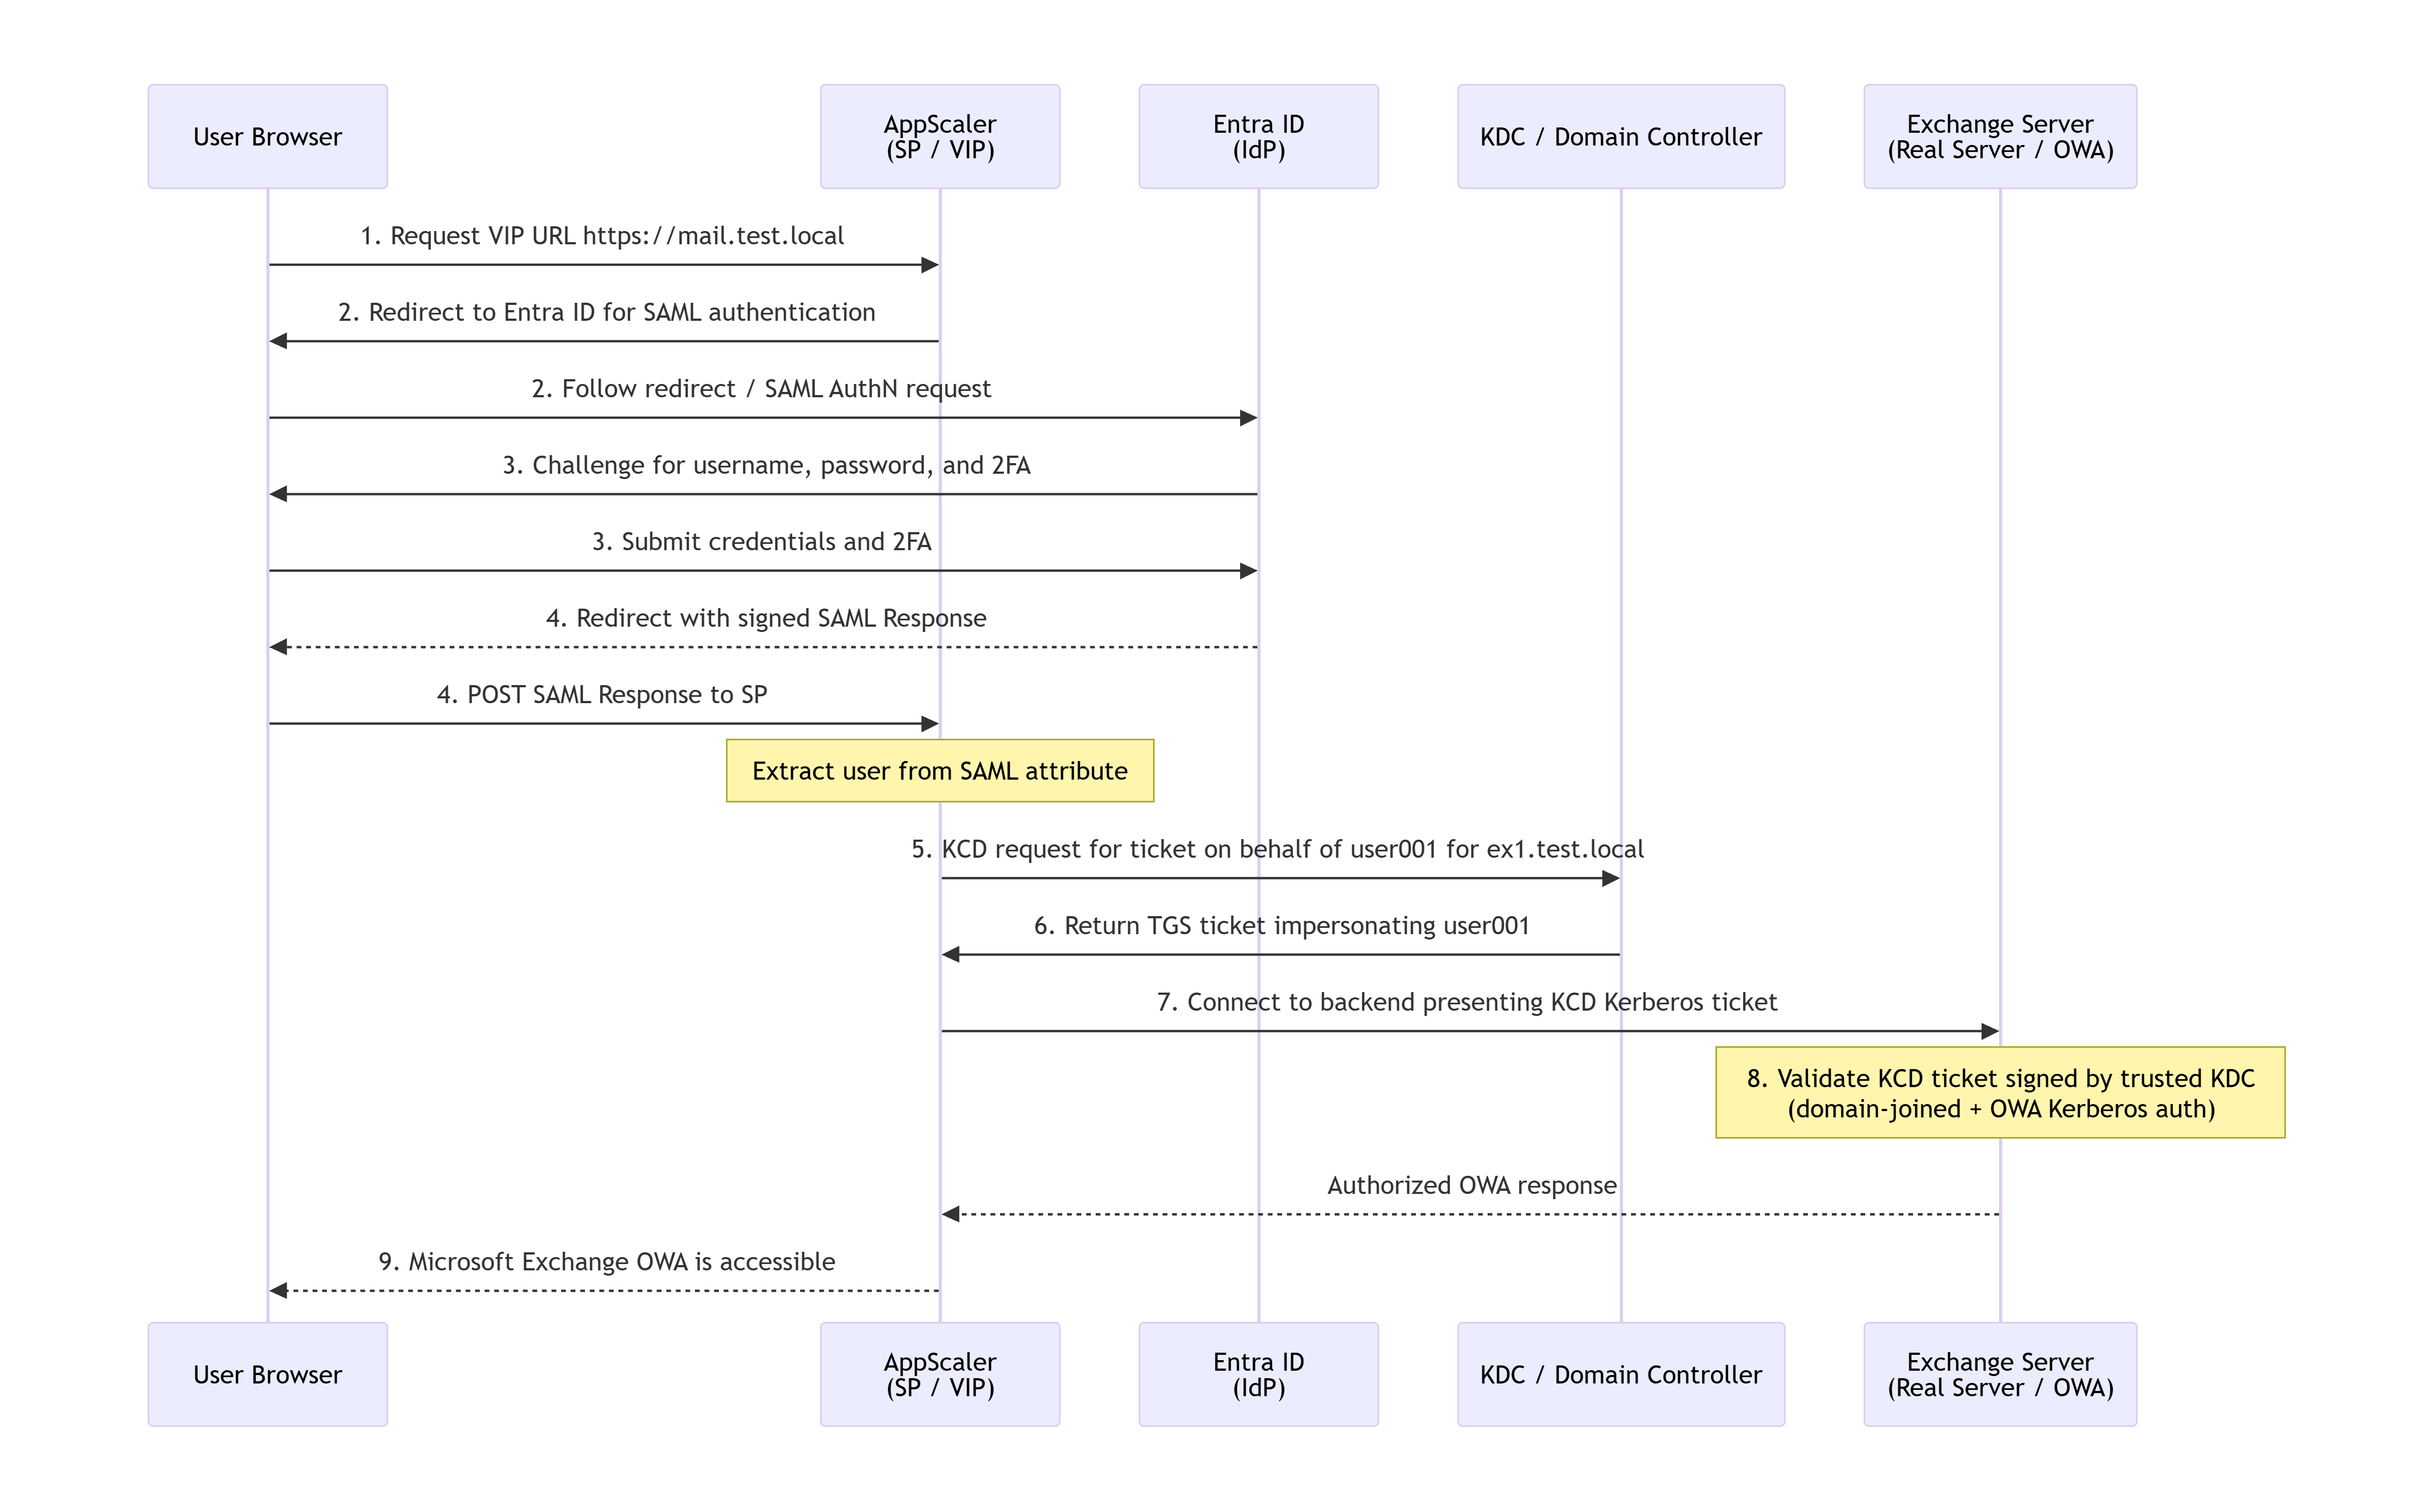
SAML via Entra ID with KCD to Microsoft Exchange
AppScaler gives you modern MFA/SSO at the front door, no password exposure to the proxy or backend, constrained Kerberos delegation to Exchange, and seamless OWA access for a wide range of clients:
- Modern SSO with Entra ID
- MFA and Conditional Access enforced by the IdP
- Seamless Kerberos SSO to Exchange OWA
- Constrained delegation for least privilege
- Works for non-domain-joined and BYOD clients
- Backend Exchange remains Kerberos-only
- Both authentication and authorization are performed using SAML
- Reverse proxy security and scalability
- Centralized policy and auditing
- Hybrid identity friendly
- Better user experience
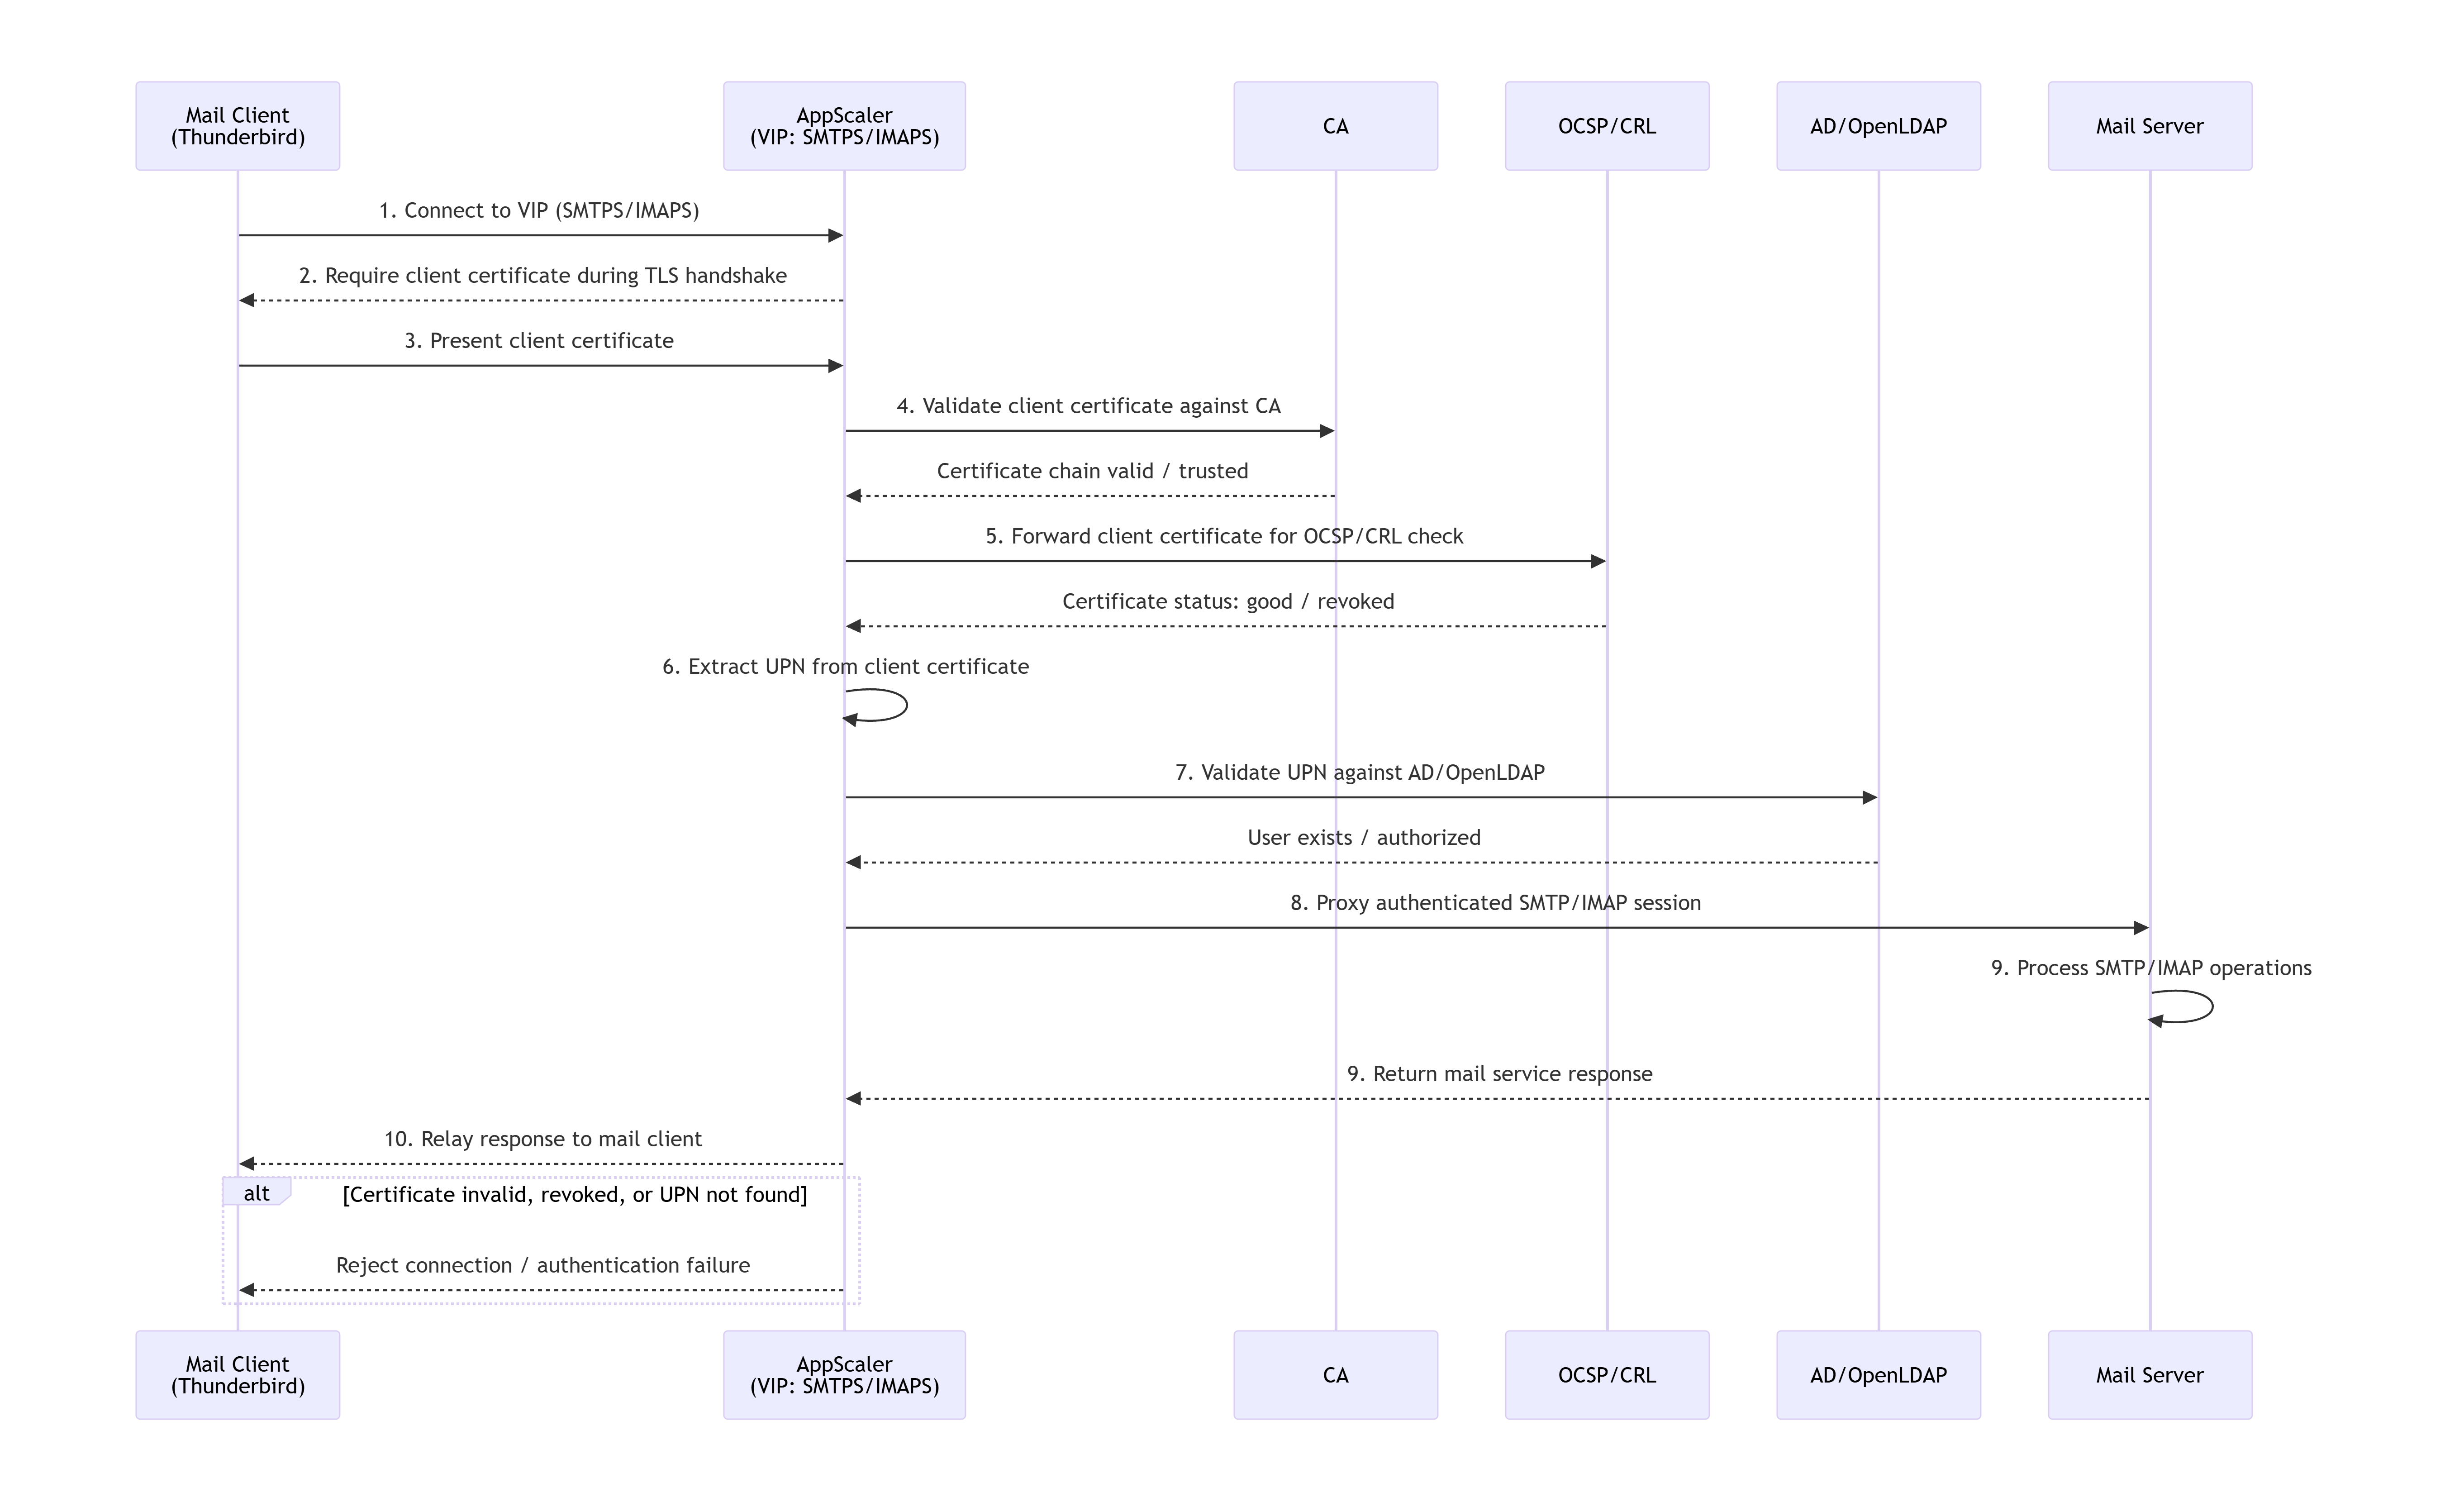
SMTP/IMAP/POP3 AAA
AppScaler AppScaler enforces mutual TLS (mTLS) with client-certificate authentication, validates the certificate against the enterprise PKI, checks revocation status, maps the certificate to a directory user, and then proxies the authenticated session to the mail server:
- Strong, passwordless authentication using client certificates.
- Centralized enforcement of certificate validation and revocation checks.
- Integration with existing PKI, AD, and OpenLDAP.
- Offloads TLS and certificate handling from the mail server.
- Supports zero-trust and compliance requirements for email access.
- Scalable and highly available when AppScaler is deployed as a VIP with load balancing.

Highest Performing Application Delivery Controller
XPoint's AppScaler outperforms most of the best technology available at any price. Our products are deployed largely in rigorous Banking/Financial Services and Service Providers environment to provide the fast, available, and secure application delivery.
With FPGA based hardware models, AppScaler can easily meet the low latency and jitter requirements of financial applications.

Zero Trust Strategy for Securing Applications
AppScaler identity access proxy provides authentication and authorization for your organizations employees and users. You can use it to incorporate single sign-on, multi-factor authentication, and access management services right into your applications.
Our unique approach to application security looks at the who, what, where and when resources are being accessed. It allows you to delivera consistent user experience across on-premise and cloud applications

The Most Feature-Rich Application Delivery Controller
AppScaler provides unmatched load balancing, application acceleration, and user authentication to optimize mission-critical business application performance and visibility:
A trusted Parnter on Application Delivery Solutions

Azania Bank Limited is the first indigenous private bank in the United Republic of Tanzania, formerly known as 1st Adili Bancorp Limited established in 1995 following the liberalization of the banking sector.
The bank needed all transactions to be SSL encrypted for security and compliance which significantly increased the burden on the servers, and users at various geographic locations experienced slow application responses. This results in lost revenue, decreased productivity and unhappy customers
The bank selected AppScaler 2020 appliance:
- 800% increase in SSL transaction capacity with AppScaler 2020
- 6X accelerated user experience
- 99.999% high availability
Ready to Learn More About AppScaler? Our experts are here to help.